Cybersecurity Compliance Support for Defense Contractors
Government contractors are under increasing obligation to satisfy federal cybersecurity requirements before they can qualify for defense work. Anderson-Reaux Technical Solutions in Boonsboro draws on more than thirty years of combined expertise to guide organizations through the Cybersecurity Maturity Model Certification process with clarity and precision. Our specialists collaborate directly with your team to identify compliance shortfalls and secure sensitive defense data. We verify more than 10,000 individual controls to ensure your systems are fully prepared for audit review. For any organization operating within the defense industrial base, failing to achieve certification can result in complete loss of contract eligibility. That is why partnering with a proven provider of professional CMMC 2.0 Compliance in Boonsboro can have a lasting impact on your organization's competitive position. We provide structured gap assessments, targeted policy creation, and continuous environmental monitoring customized to your security landscape. Our approach allows your staff to remain focused on business priorities while we maintain the integrity of your cybersecurity posture.
Defense Industrial Base Requirements, Certification Levels, and Compliance Assessments
Powerful features designed for modern teams
Breaking Down CMMC 2.0 Certification Levels and Their Requirements
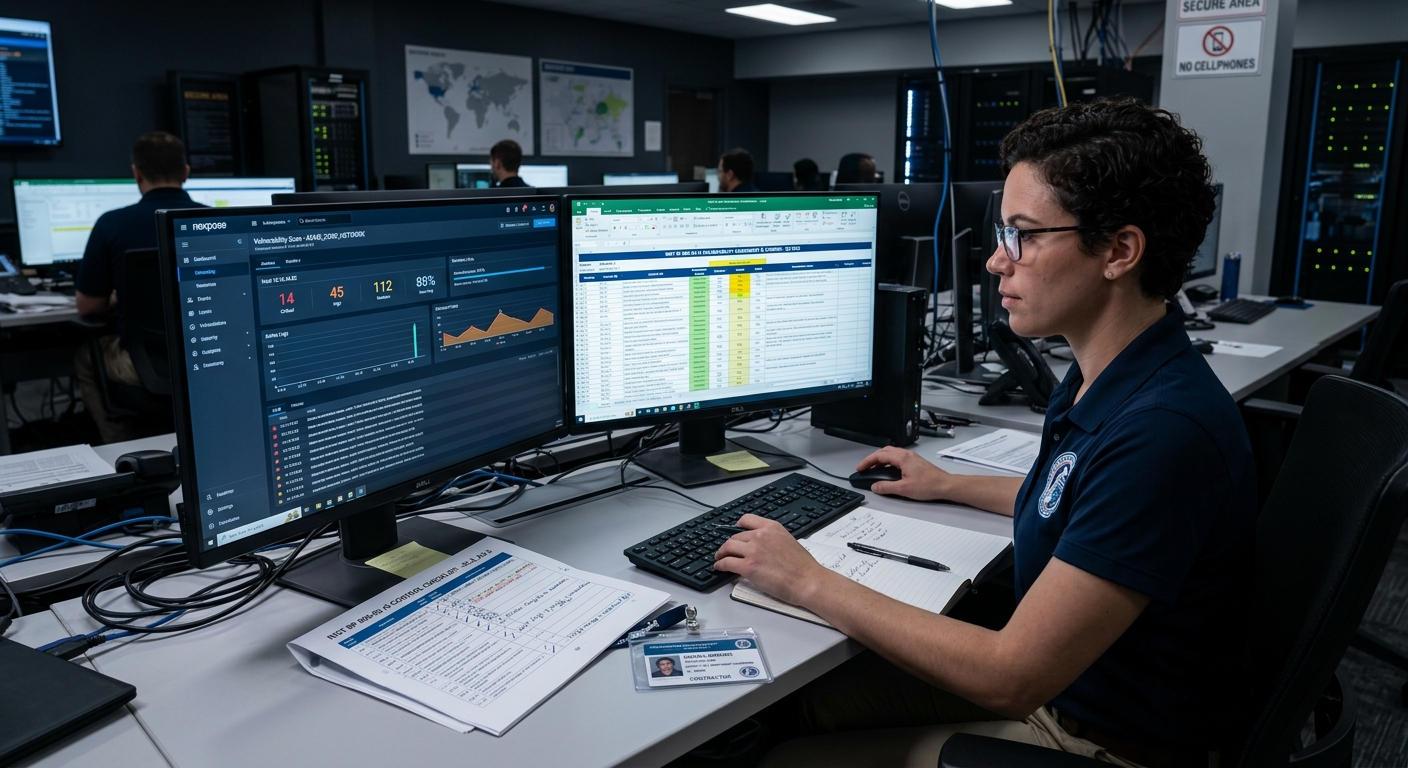
Conducting NIST SP 800-171 Gap Assessments and Understanding SPRS Scores
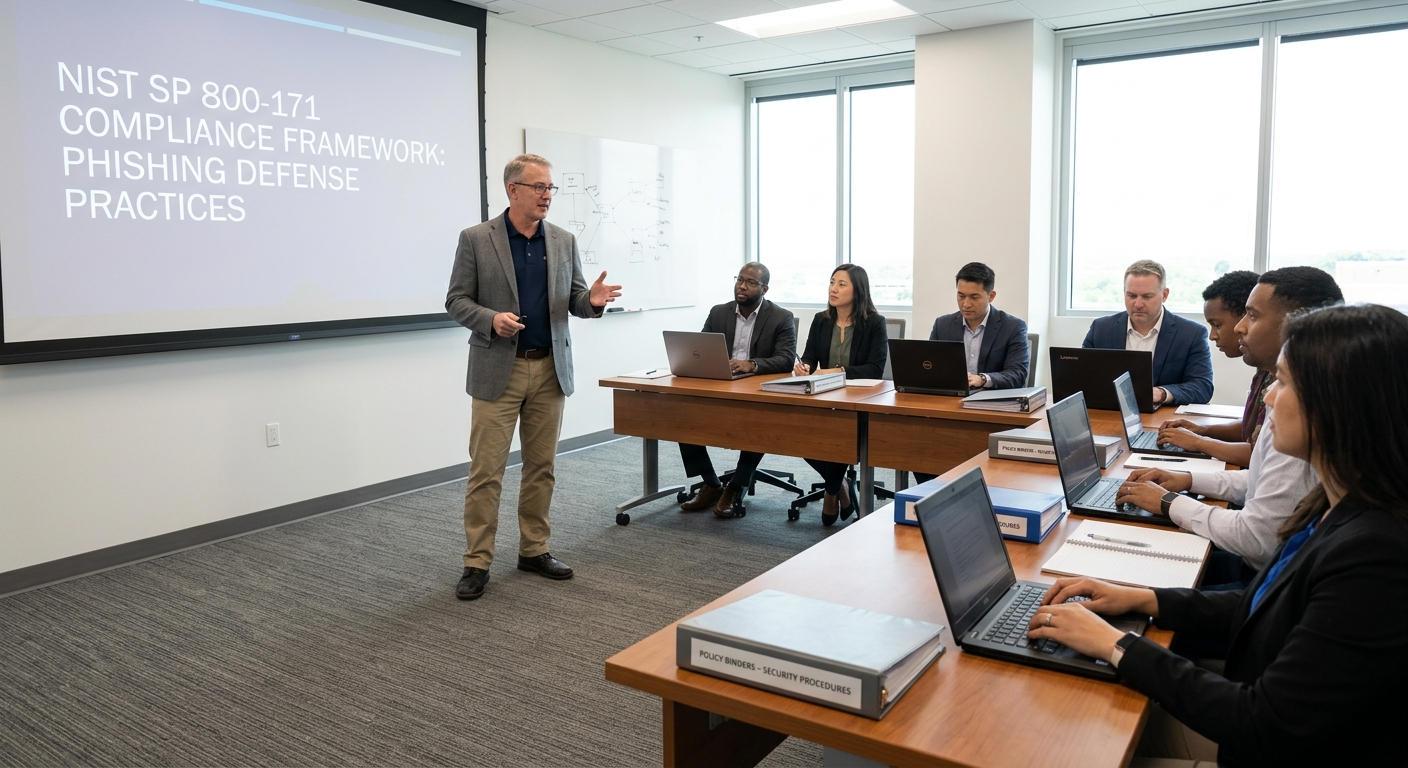
Policy Development, Workforce Training, and Continuous Monitoring for Lasting Compliance
Frequently Asked Questions
CMMC 2.0 is the Department of Defense's revised certification framework that mandates contractors meet defined cybersecurity standards before they are permitted to handle sensitive defense information. Organizations that fail to achieve certification risk losing their ability to compete for federal contracts altogether.
The current framework is organized into three tiers. Level 1 addresses fundamental cyber hygiene practices, Level 2 requires full alignment with NIST SP 800-171, and Level 3 is designed to counter sophisticated threats directed at contractors working on the most sensitive defense programs.
An SPRS score is a numerical indicator the DoD uses to evaluate how well a contractor's cybersecurity posture measures up against established standards. A low or negative score signals unresolved security weaknesses and can prevent an organization from winning or keeping government contracts.
The duration depends on an organization's scale and its existing security infrastructure, but most assessments are finalized within several weeks. The outcome is a clear, prioritized remediation plan that targets the controls with the greatest influence on overall compliance readiness.
Yes. choose Anderson-Reaux Technical Solutions validates over 10,000 controls and assembles the documentation, policies, and evidence packages that auditors require to confirm your organization satisfies every mandated cybersecurity practice ahead of a formal third-party assessment.
Ready to Transform Your Business?
Join thousands of companies already using our platform